Explore in 3D
Turn it over
before you specify it.
Seven of the instruments below are modelled in three dimensions. Drag to rotate, scroll to zoom, and hover any marker to read what that part of the machine does.
 3D · Interactive
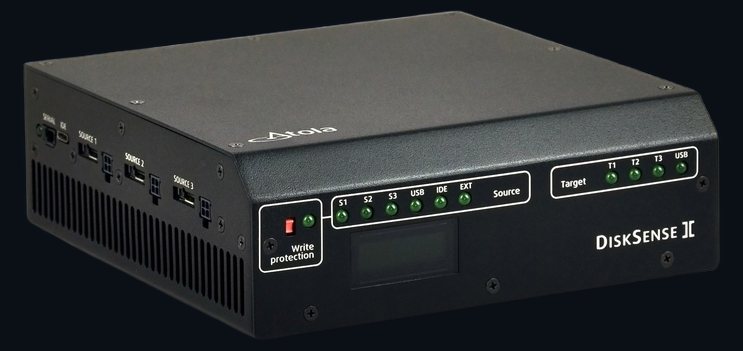
Atola Insight Forensic
The first and only forensic acquisition tool that works with both good and damaged media.
Open the model →
 3D · 2 builds
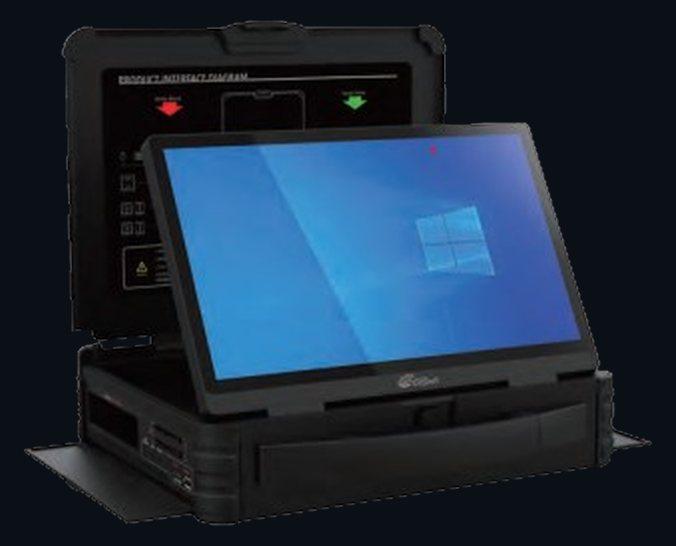
Forensic Cube V4
All you need for on-scene investigation — a write-blocked forensic workstation in a case one person carries.
Open the model →
 3D · Interactive
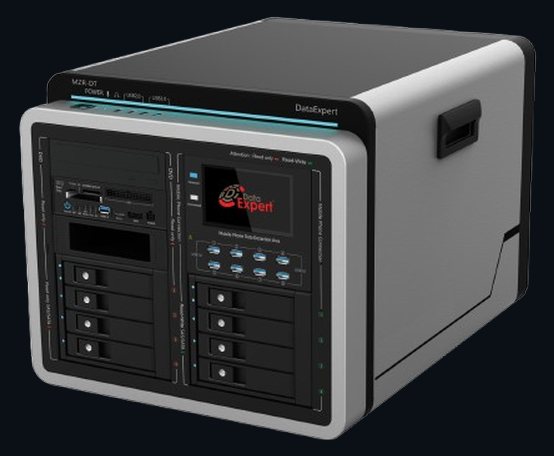
Cyber MZR-DT
All-inclusive forensic workstation for rapid analysis of artifacts.
Open the model →
 3D · Interactive
Cyber MZR-X
All-in-one solution for a digital forensic laboratory — the bench itself, not a box that sits on one.
Open the model →
 3D · 2 builds
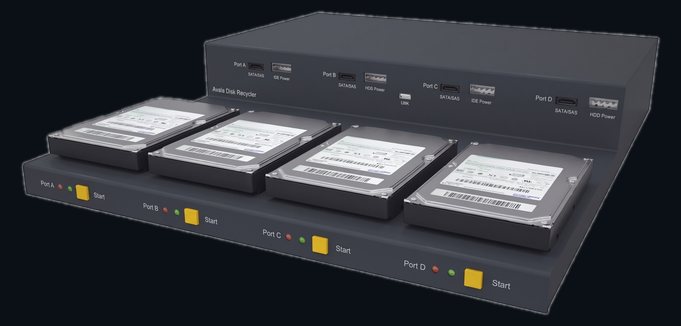
Atola Disk Recycler
Scriptable high-speed SAS, SATA and IDE hard drive tester, wiper and repairer.
Open the model →
 3D · Interactive
NSA Degausser MagWiper
Fast, safe and portable — and on the NSA’s own evaluated products list.
Open the model →
 3D · 3 builds
Degausser 30X / 25X / 15X
One field, three chambers — pick the one that matches the volume you actually have to clear.
Open the model →
Catalogue
Everything we carry
18 instruments across three disciplines. Select any one for its full specification, and the manufacturer's brochure where we hold it.
Data Recovery & Digital Forensics12 products
DEY-AIF
Atola Insight Forensic
All-in-one system for professional data recovery and forensic acquisition, with ATA password removal, firmware recovery and a built-in write blocker.
View details →
MZR-P
Forensic Cube V4
Portable forensic workstation with a built-in multi-interface write blocker, 14-inch touch screen and D-Box imaging software, in an army-grade case.
View details →
Cyber MZR-DT
Cyber MZR-DT
Workstation-class forensic bench: write-blocked and read/write drive bays, a multi-interface blocker, and an eight-port phone extraction panel in one case.
View details →
Cyber MZR-X
Cyber MZR-X
A complete forensic workstation built into the desk: write-blocked and read/write bays, an eight-port phone panel, document and task cameras, and two 34-inch curved displays.
View details →
 MagiCube V3
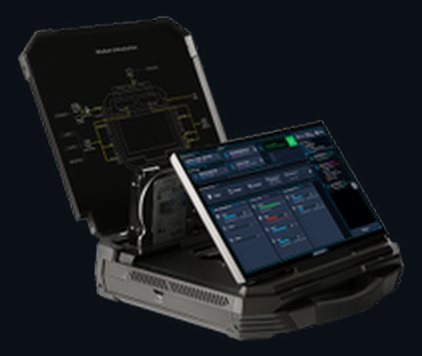
DataExpert MagiCube
Portable forensic unit combining hard disk duplication, forensic analysis and live OS emulation behind an 11.6″ touchscreen.
View details →
 DEM-FT
DataExpert Forensic Tower
Parallel Forensic Technology reaches 27 GB/min — four-channel parallel clone or eight-channel parallel analysis, with eight built-in write blockers.
View details →
 RECON
SUMURI RECON
Finds and parses Mac artefacts automatically, builds advanced timelines, and recovers Keychain passwords in minutes rather than weeks.
View details →
 CARBON
SUMURI CARBON
Boots any Windows machine as a virtual machine in minutes — no forensic image first, no disassembly, and logon passwords bypassed on the way in.
View details →
 RECON IMAGER
SUMURI RECON Imager
Images all Intel-based Macs including APFS, handles FileVault encryption, and captures Mac RAM without an administrator password.
View details →
 Digital Evidence Investigator
ADF Digital Evidence Investigator
Prioritises and collects files and artefacts fast, and presents the evidence on a single timeline — in the forensic lab or on-scene.
View details →
 Triage-G2
ADF Triage-G2
ADF's award-winning media exploitation tool, deployed by special forces, military and intelligence agencies for sensitive site exploitation.
View details →
 Triage-Investigator
ADF Triage-Investigator
Automated intelligent forensic triage for field deployment alongside Digital Evidence Investigator, with a track record of court-defendable evidence.
View details →
Mobile Device Forensics2 products
 ADF MDI
ADF Mobile Device Investigator
Uses artificial intelligence and machine learning to prioritise evidence while it is still being collected.
View details →
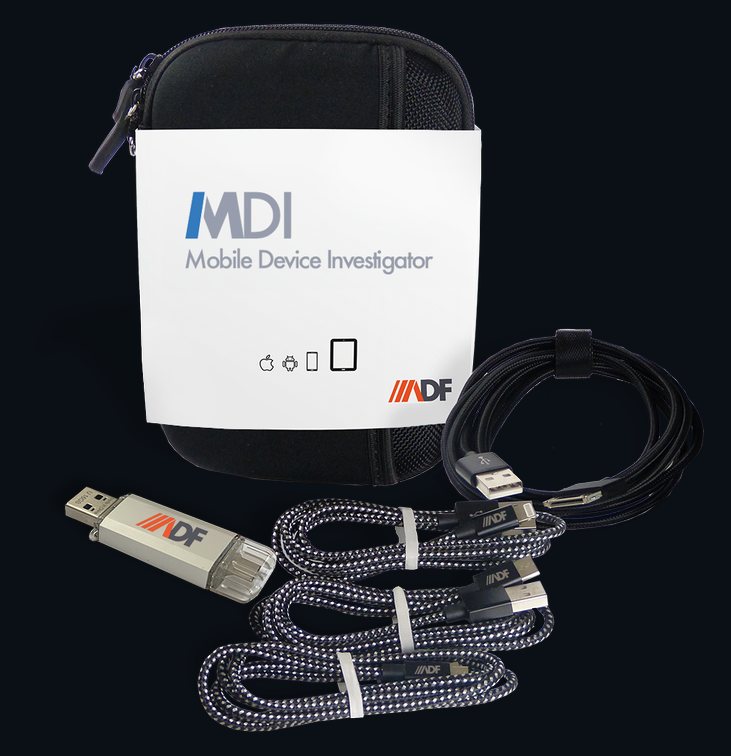 MDI Field Tablet
ADF MDI — Field Tablet
Collects evidence from iOS and Android over USB and performs an advanced logical acquisition, built for officers working away from a laboratory.
View details →
Data Security & Destruction4 products
DEY-DR
Atola Disk Recycler
Four independent ports at 470 MB/s each, scriptable, and chainable to 200 units — so decommissioning a fleet does not take a quarter.
View details →
MagWiper MW-1B
NSA Degausser MagWiper
Fast, safe, light and portable enough to take to the asset rather than move the asset to it.
View details →
DEA-MD30X / 25X / 15X
Degausser 30X / 25X / 15X
Built around an inclined plane system, with optional software auditing so each erasure leaves a record.
View details →
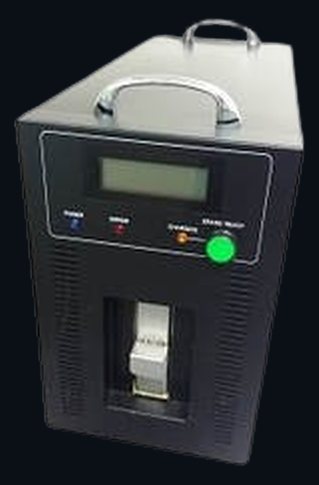 DEA-10K
Portable Degausser
Generates magnetic fields of 10,000 Oe or above for permanent erasure of hard drives and tape media on site.
View details →